Category: Technology

  • Health & Medicine in the Age of AI: Why Human Touch Still Matters in High-Tech Care

    Health & Medicine in the Age of AI: Why Human Touch Still Matters in High-Tech Care

    There is no shortage of questions regarding what AI can and cannot do. 

    From conversations surrounding the ethics of AI art to the exploration of how AI can be utilized in leadership, this year has been defined by the mass exploration of AI by professionals across sectors.

    However, very few sectors face the sheer scale of possibility as the medical and healthcare field. With scientific and medical research breakthroughs being made every day thanks to AI, we are seeing now more than ever how the technology can change the field for the better.

    And these changes stretch far beyond high-level research. We are seeing both provider-focused and consumer-facing AI tools hit the market every day, from AI scribes to robotic pill sorters. 

    Many want to push it further, with visions of AI nurses one day leading intake and streamlining care.

    The problem? Where AI encourages innovation behind the scenes, it runs the risk of stripping away the key element of patient-focused care: connection. 

    A Large Language Model (LLM) can summarize a wound note with precision, providing detailed context and making connections across the patient’s journey that would slip the notice of even the most experienced medical professionals; it can’t, however, read a patient’s reaction to bad news. Nor can it turn daily visits from medical upkeep to a vital social and emotional support for patients.

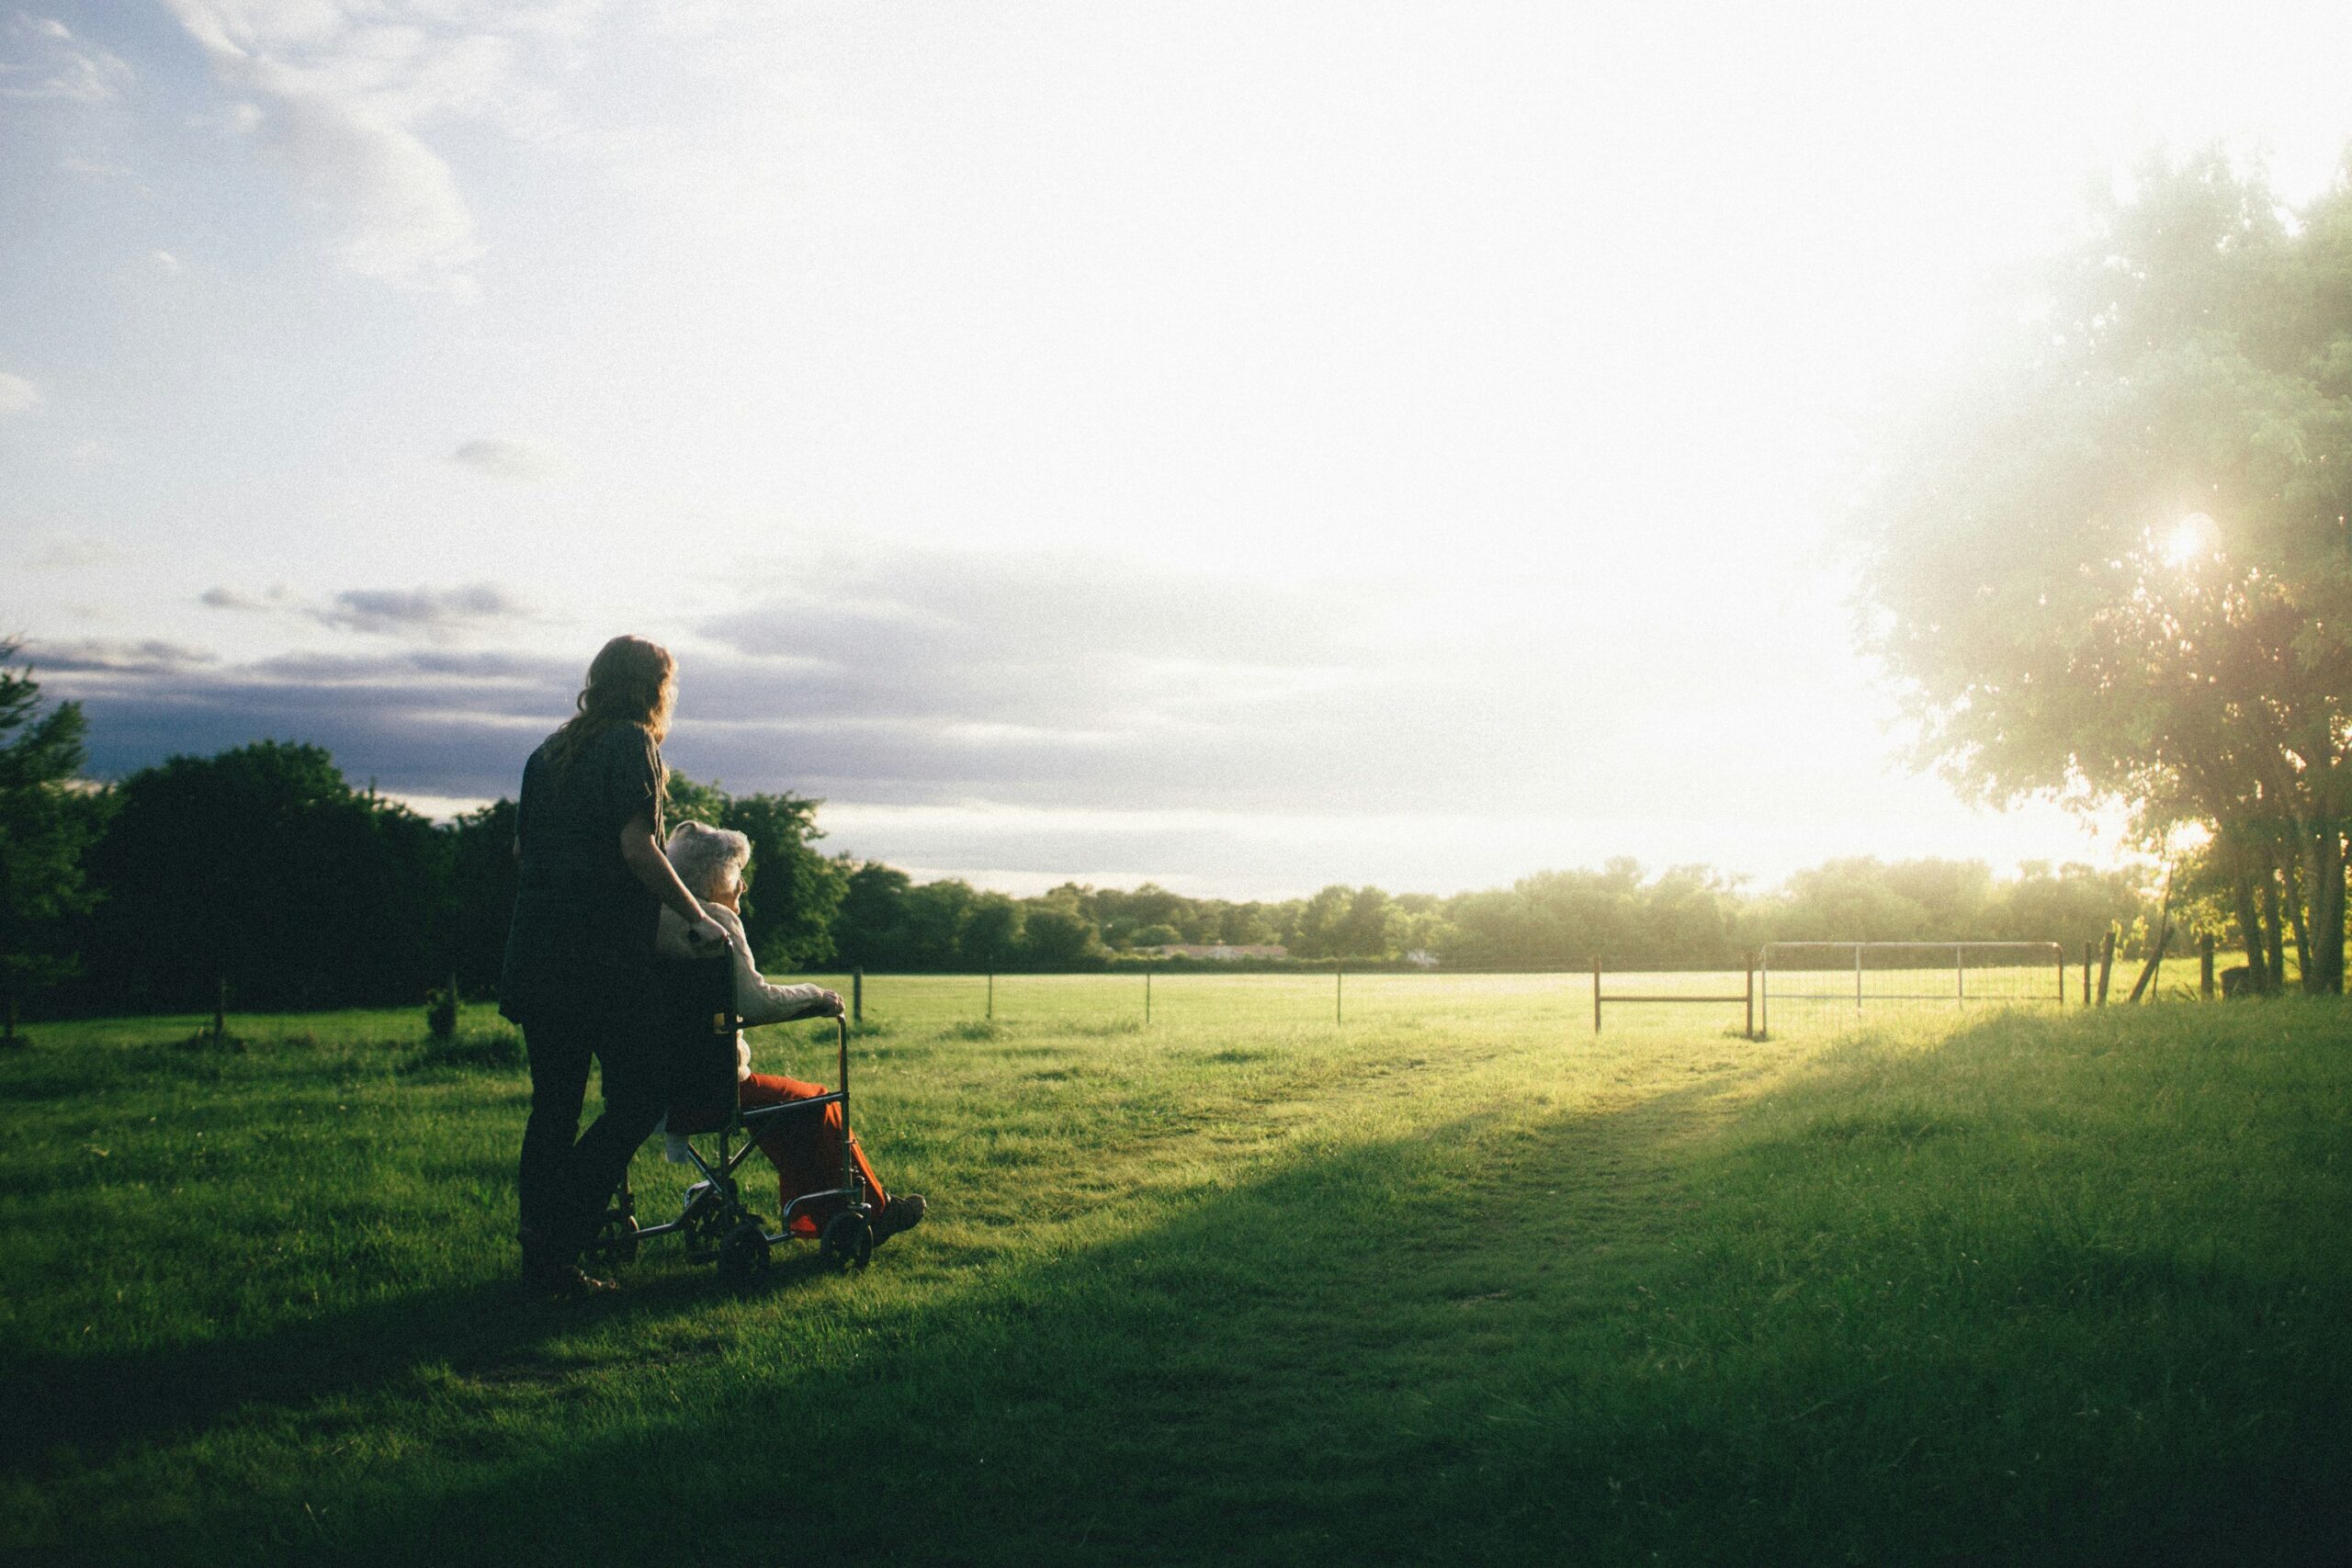
    It’s an established fact that loneliness raises mortality risk, and if there’s anything I’ve learned while owning a senior homecare referral agency, it’s that the time spent sitting and playing cards with their caregiver is just as important to a senior’s health as the help with their medication is. 

    Once, one of the caregivers we had placed told me that her “best tool” was the patient’s photo album; a source of connection that provided much-needed distraction and conversation as they administered the patient’s insulin. 

    It wasn’t a reminder app that told her when to begin the process. It wasn’t an automated dose calculator. It was a book of old photos, offering a uniquely human point of connection.

    At its core, effective healthcare has always been based on trust. As our industry takes leaps forwards in what’s possible, I think it’s important that we take the time to stop and remember the parts of medicine that can’t be replaced with an algorithm: Rapport. Humanity. Connection.

    This isn’t to say that AI nurses couldn’t one day play a hugely important role in a robust healthcare journey. I am a firm believer that Artificial Intelligence is exactly the push we’ve been needing to bring healthcare into the future. Let it draft notes, chase prior authorizations, predict who needs a check in, spot patterns, and provide warning in cases that may go otherwise unnoticed. But to forgo AI’s human counterparts completely doesn’t speak to innovation; it creates a clinical space that is just that: purely clinical, with none of the human touch that every patient needs.

    But, if done correctly, we could be building a future that is both high-tech and high-touch.
  • Why Hackers Understand Human Nature Better Than Most Leaders

    Why Hackers Understand Human Nature Better Than Most Leaders

    Cybersecurity isn’t really about firewalls or encryption. It’s about people.

    And the uncomfortable truth is that hackers—whether sophisticated nation-state actors or opportunistic phishers—understand human nature far better than most corporate leaders ever have. They exploit curiosity, urgency, trust, ego, and fear. Meanwhile, too many executives still believe cybersecurity is just a technical problem that IT can “patch.”

    The psychology behind the breach

    When I was at Red Sift and Valimail, we watched attacks evolve; not because the technology changed first, but because attackers’ understanding of people did. Social engineering—phishing, pretexting, business-email compromise—still accounts for the majority of successful intrusions. According to the U.S. Cybersecurity & Infrastructure Security Agency (CISA), over 90% of successful cyber incidents begin with a human-enabled action, such as clicking a malicious link or misconfiguring access rights (CISA Annual Report 2023).

    Hackers don’t brute-force systems anymore; they brute-force psychology. They study how employees communicate, how leadership pressures teams for speed, and how routine creates complacency. They mimic your vendors, your CEO’s writing style, your invoicing cadence. In short, they don’t just hack code—they hack context.

    Why leadership culture creates opportunity

    Here’s the part most leaders miss: every successful breach tells a story not only of technical failure but of organizational behavior.

    • Speed over security: When management celebrates instant replies and “always-on” responsiveness, employees hesitate to verify suspicious messages.

    • Complex processes: Lengthy password resets or clunky VPN logins lead people to find workarounds.

    • Low psychological safety: If people fear punishment for mistakes, they hide incidents—giving attackers more time to exploit them.

    The 2023 Verizon Data Breach Investigations Report found that 74% of breaches involved a human element—errors, misuse, or social engineering. That statistic hasn’t budged much in years, even as security spending soars. Clearly, technology isn’t the limiting factor. Human nature is.

    How hackers harness empathy and narrative

    Successful attackers are, ironically, great storytellers. They craft believable micro-narratives—an unpaid invoice, a shipping delay, an urgent HR message. They use empathy as a weapon: “I’m just trying to help you solve this problem quickly.” That small emotional bridge is all they need.

    At Red Sift, one of our simulated phishing tests exploited compassion. We sent employees a fake email titled “Help our colleague in crisis” with a donation link. Click rates spiked to 68%. No exploit kit, no malware. Instead? Basic human psychology. Empathy used as leverage.

    Turning awareness into resilience

    So what should leaders do differently? Here’s what I’ve learned from leading go-to-market teams in cybersecurity companies:

    1. Model security behavior at the top
      If the CEO still reuses passwords or ignores MFA prompts, every awareness campaign will fail. Leadership’s daily habits set the baseline for cultural norms.

    2. Design for frictionless security
      Security that slows work will be bypassed. Invest in identity automation, passwordless systems, and secure-by-default workflows. At Valimail, we saw adoption soar when email authentication required zero user action—security became invisible.

    3. Shift from compliance to culture
      Annual training slides don’t change habits. Storytelling does. Share anonymized internal “near-miss” incidents. Make security personal, not procedural.

    4. Reward reporting, not silence
      Celebrate the employee who reports a phishing attempt, even if they clicked first. Fear kills disclosure; disclosure saves the network.

    5. Fuse cybersecurity with leadership training
      Managers must understand behavioral risk as deeply as financial risk. Cyber awareness isn’t IT literacy—it’s emotional intelligence under pressure.

    What organizations like Hallmark Homecare and CareFortis reveal

    Healthcare is a perfect test case. Hallmark Homecare and CareFortis operate in environments where lives—not just data—are at stake. Both have invested in training clinicians and administrators to recognize social-engineering cues. Yet, they also learned that stress, fatigue, and urgency—common in healthcare—make staff more susceptible to manipulation.

    According to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights, healthcare breaches rose 93% between 2018 and 2023, with an average cost per incident exceeding $10 million (HIPAA Journal 2024). The biggest driver? Human error. This points to something far greater than a mere IT problem; it reveals an an organizational empathy gap.

    The leadership lesson

    Hackers understand that the shortest path to your data runs through your people. They study incentive structures, communication tone, and cultural blind spots. Leaders who ignore these soft factors are, unintentionally, on the hacker’s side.

    True cybersecurity leadership starts with humility—accepting that people, not systems, are the front line. It demands curiosity about human behavior, not just technical architecture. It means building cultures where trust and vigilance coexist.

    Hackers already know that every organization is only as secure as its most distracted moment. The question is: do your leaders know it too?